Skip to content

25 Products

Explore products
AI Powered GRC

One platform.Every line of defence.

XpediOo GRC & ERM Suite unifies Third Party Risk, Internal Audit, Enterprise Risk, Compliance, Governance, Privacy, Business Continuity, Cybersecurity and Model Risk into a single AI native system of record, replacing spreadsheets, email chains and disconnected point tools.

All products
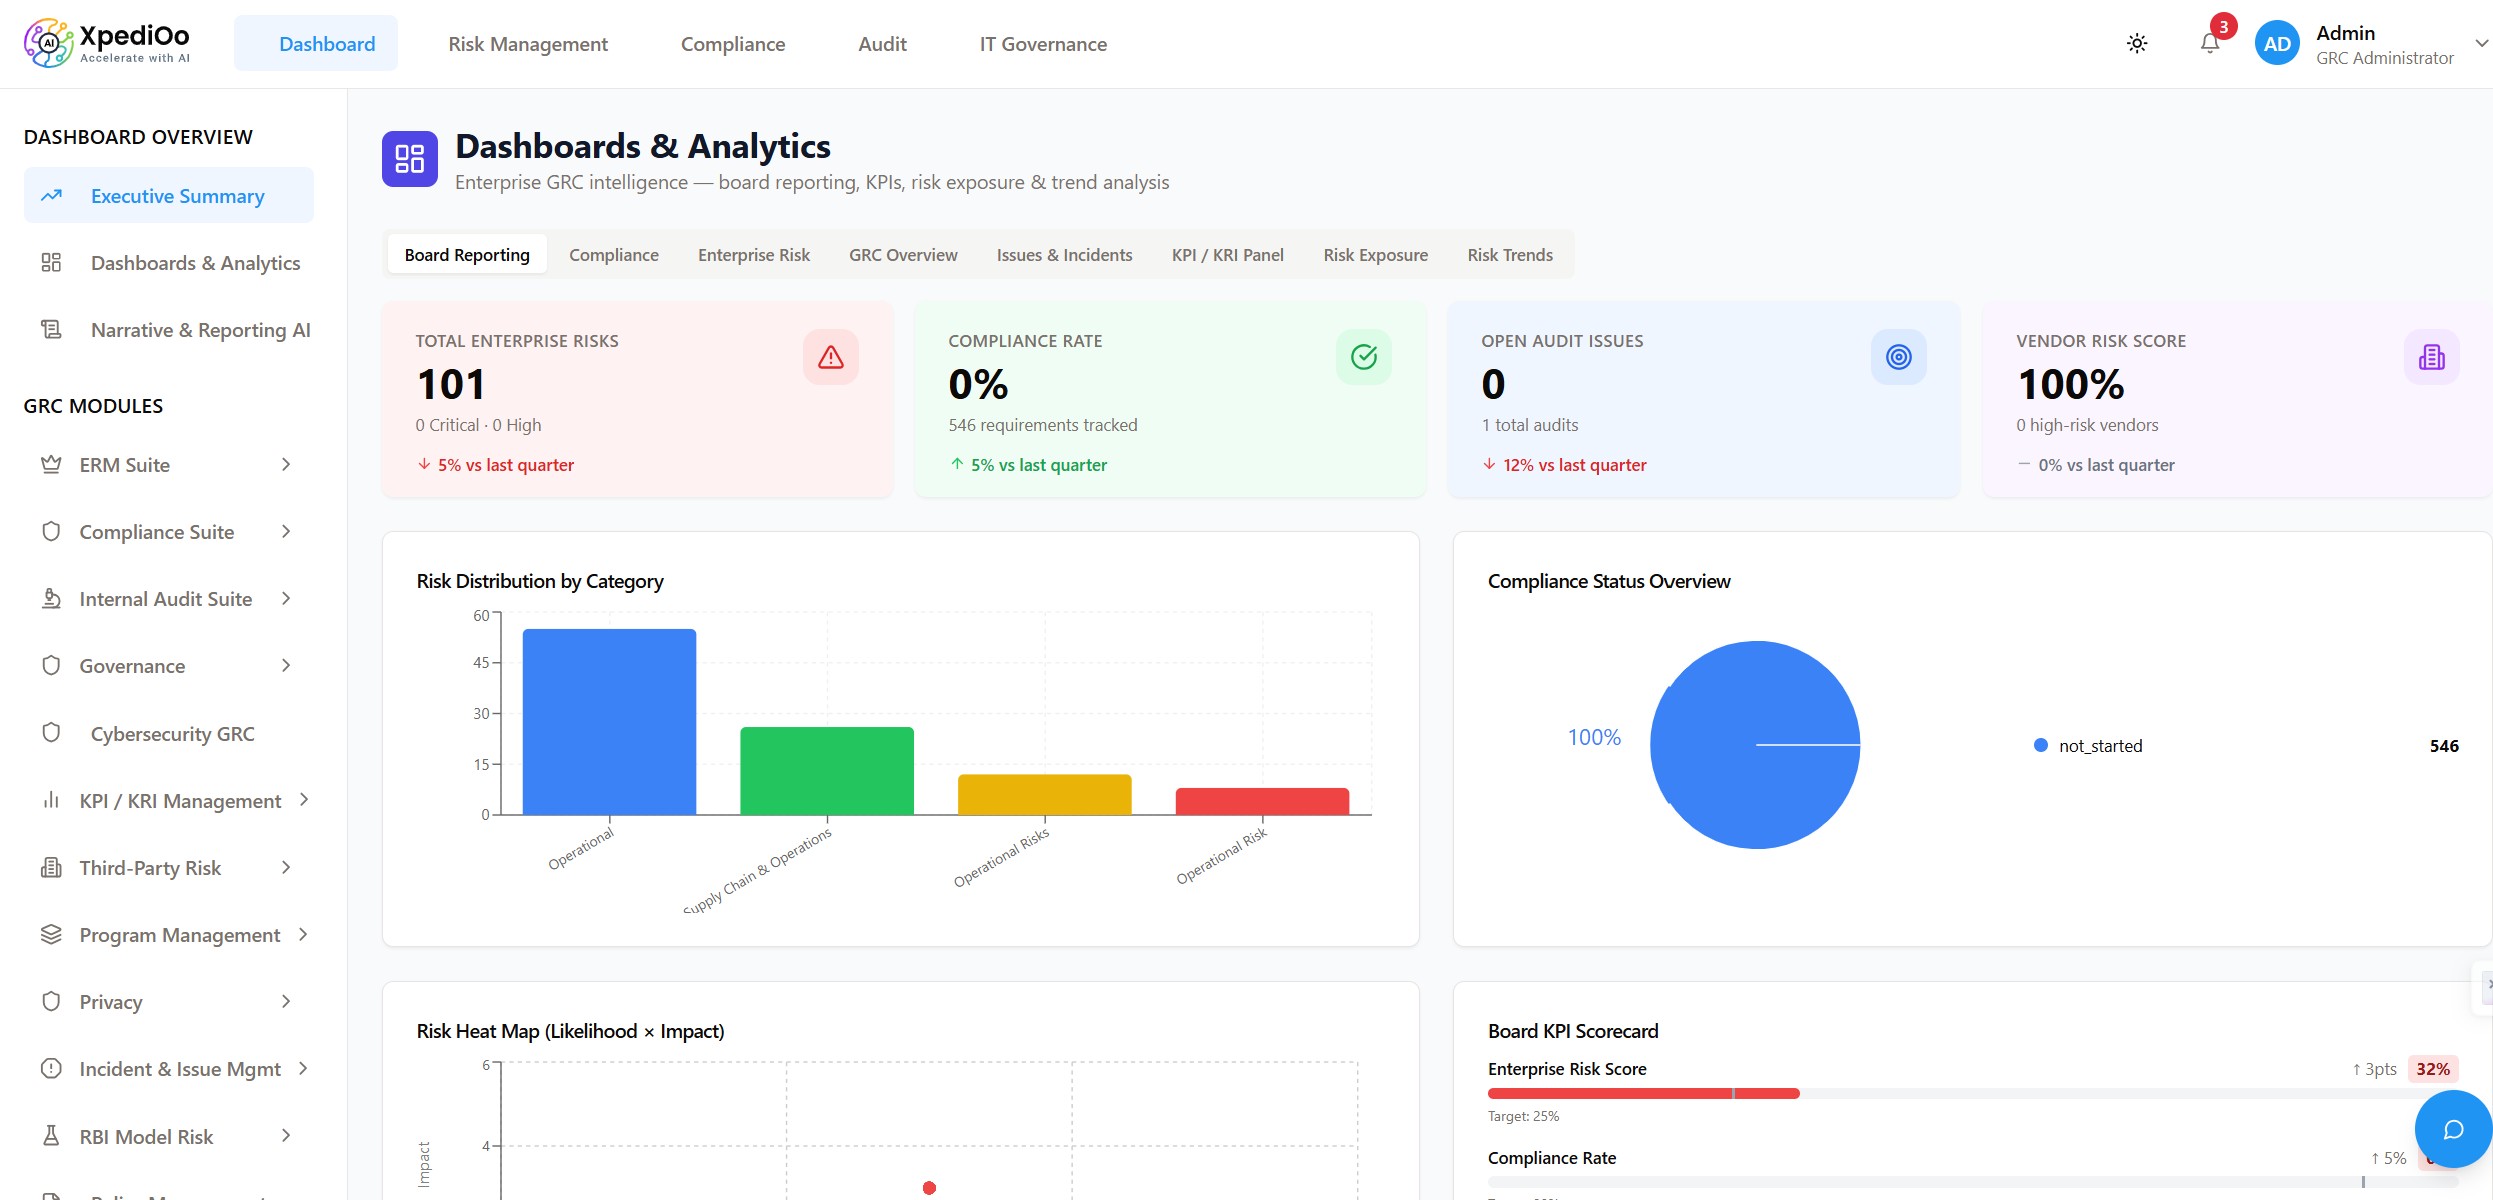
Executive GRC Dashboards & Analytics
XpediOo GRC Dashboards and Analytics executive overview with risk, compliance, audit, and vendor metrics

Executive GRC Dashboards & Analytics

See total enterprise risk, compliance rate, open audit issues, vendor exposure, risk distribution, and board KPI scorecards at a glance.

210
Regulatory frameworks
20+
Purpose built modules
60+
Dedicated AI endpoints
8
Supported LLM providers
Platform and trust

An AI native architecture, built for sensitive data

Every module shares one data model, one AI engine and one evidence store, so risk, compliance, audit and vendor data reinforce each other instead of living in silos.

Platform architecture

  • Unified data model. Risks, controls, vendors, findings, policies, obligations, incidents and evidence are related records, not disconnected spreadsheets.
  • Bring your own AI provider. OpenAI, Anthropic, Google AI, NVIDIA, DeepSeek, Amazon Bedrock, Meta Llama and custom endpoints, with connection testing before go live.
  • Model Context Protocol (MCP) server exposes live risk, compliance, audit, vendor and policy data (plus full risk CRUD) to approved AI clients like Claude Desktop, Cursor and Windsurf.
  • Evidence first design. Uploaded contracts, questionnaires, SOC 2 reports and audit workpapers are read by AI, not just stored.
  • Role based, framework aware. 210 regulatory and standards frameworks modelled natively across audit, compliance, policy and cyber modules.

Security, data and deployment

  • Authenticated by default. Every API sits behind session based authentication; exceptions like a vendor's one time questionnaire link are narrowly scoped, tokenised and expire on submission.
  • Centralized evidence storage. Contracts, SOC 2 reports, audit workpapers and questionnaire attachments live in a dedicated object storage layer with per record linkage.
  • Administrator controlled AI. LLM Settings gives full control over which provider and model power every AI feature, with masked credentials and connection testing before go live.
  • Governed AI to data access. The MCP server is protected by its own API key and exposes a documented, filterable tool catalog rather than open database access.
  • Role aware by module. Identity Governance provides permission matrix role modelling, business unit segmentation and MFA enrolment tracking.
  • Deploys as one application. A single, centrally hosted web app with one system of record; no per module install or data sync job to maintain.
Compliance coverage

Supported Frameworks, by domain

Explore a selection of our 210 supported regulatory frameworks and standards. Select a badge to see its scope, practical uses and advantages.

Privacy

Personal data and privacy management.

Cybersecurity

Security management, baselines and threat coverage.

Governance

Board oversight, internal control, risk reporting and organizational governance.

AI

AI management, risk and governance.

Pharma & GxP

Medicine manufacturing, API quality, pharmaceutical quality systems and electronic records.

Manufacturing

Quality, automotive and aerospace, worker safety, environment and industrial OT security.

GRC in action

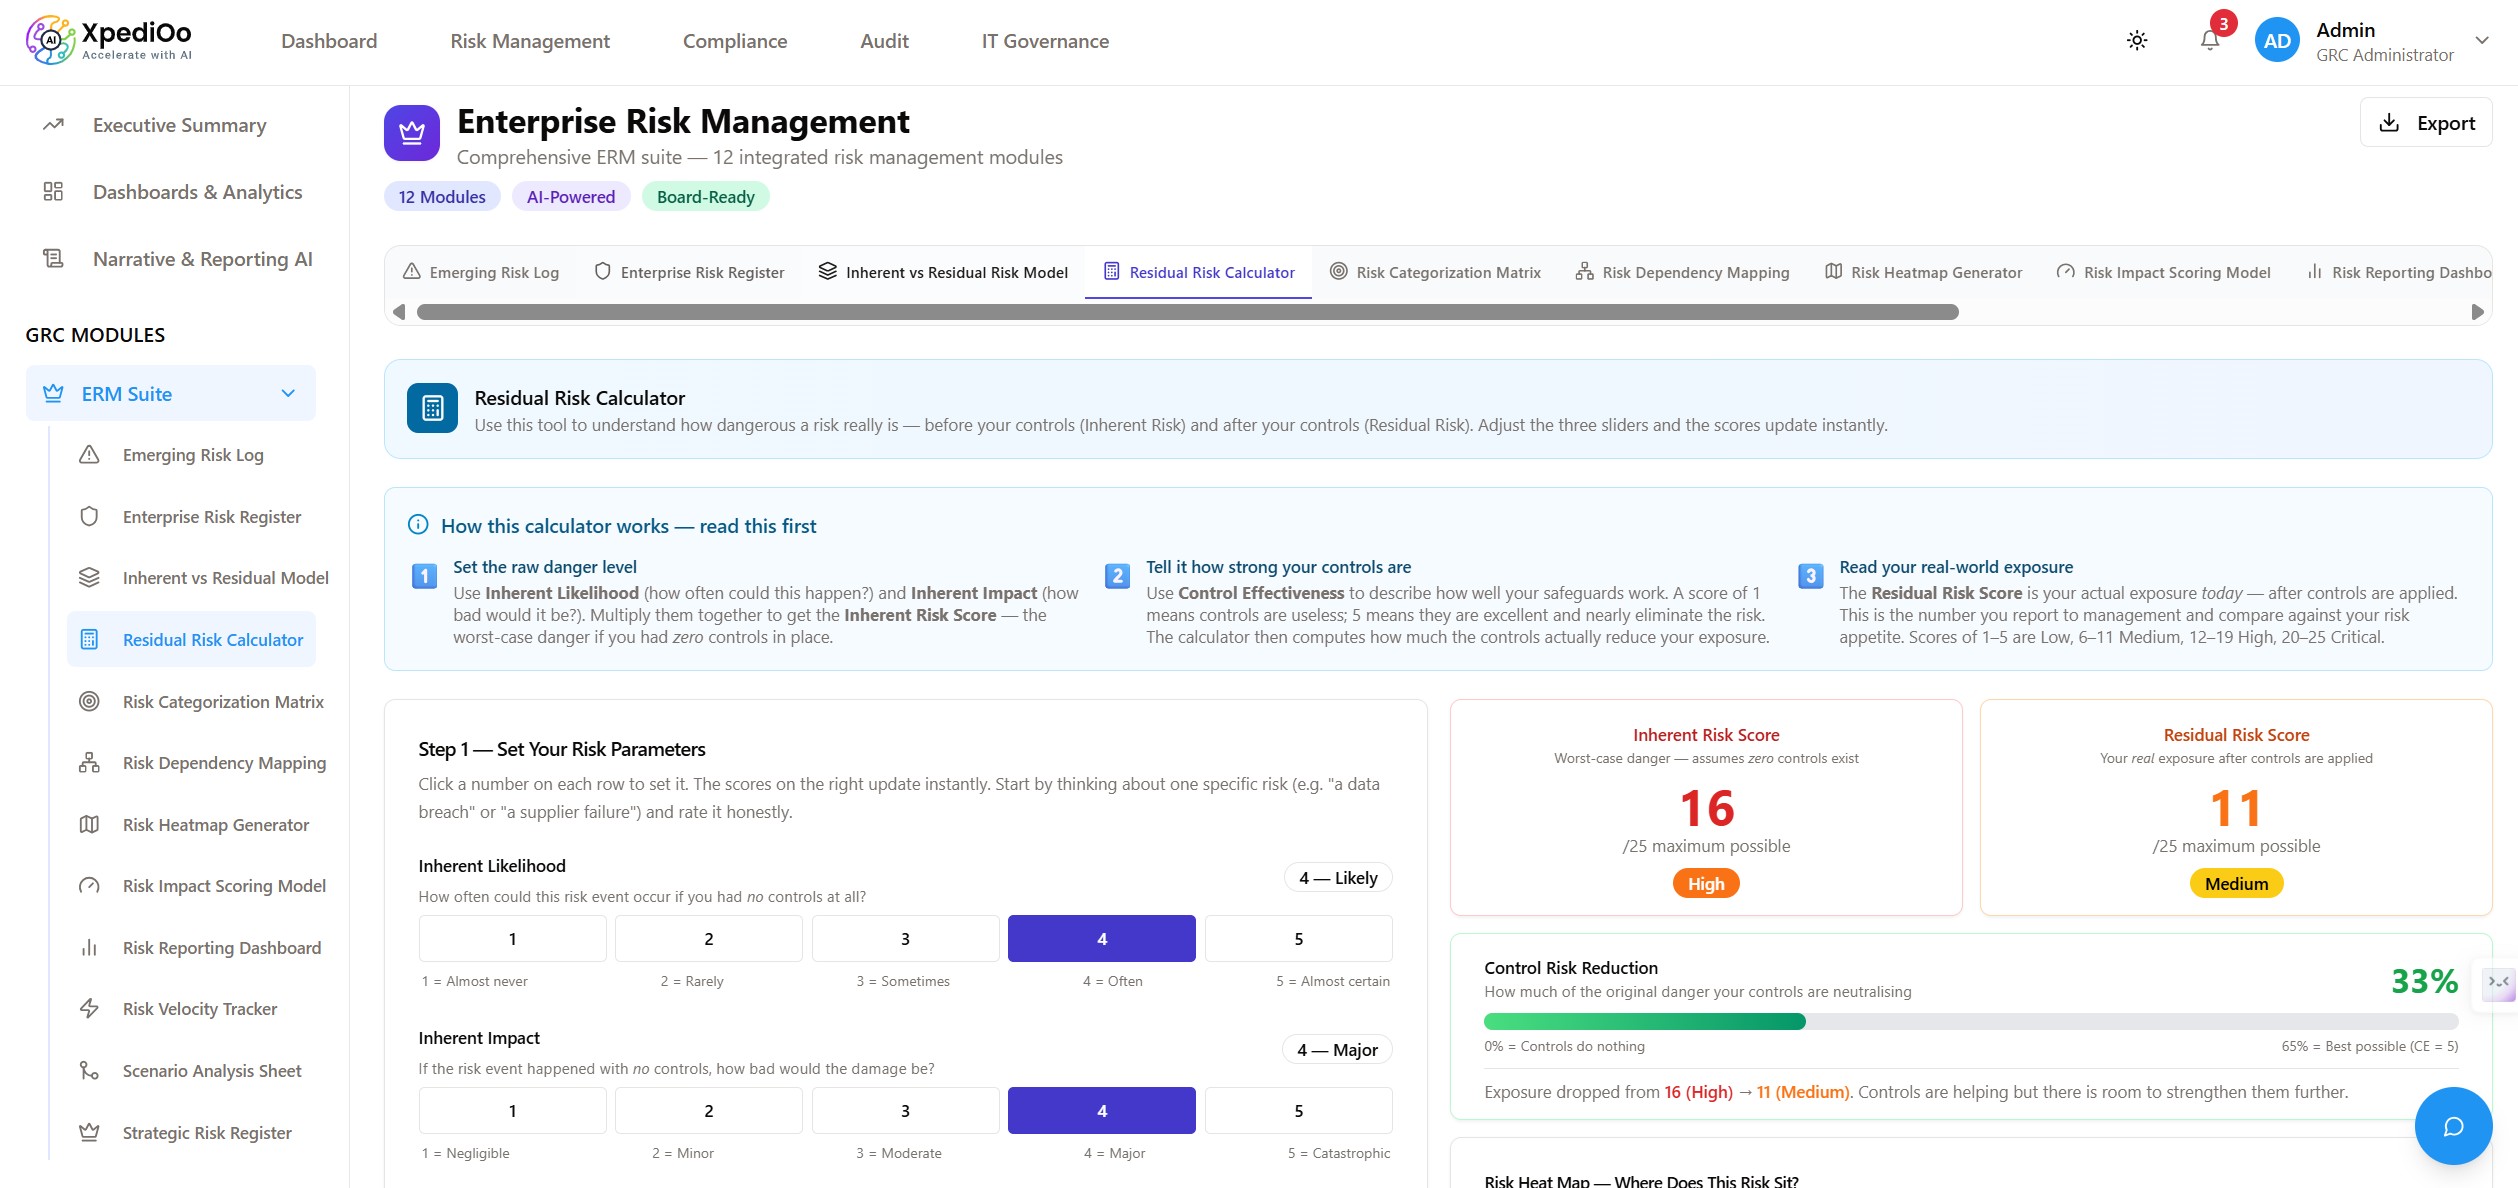
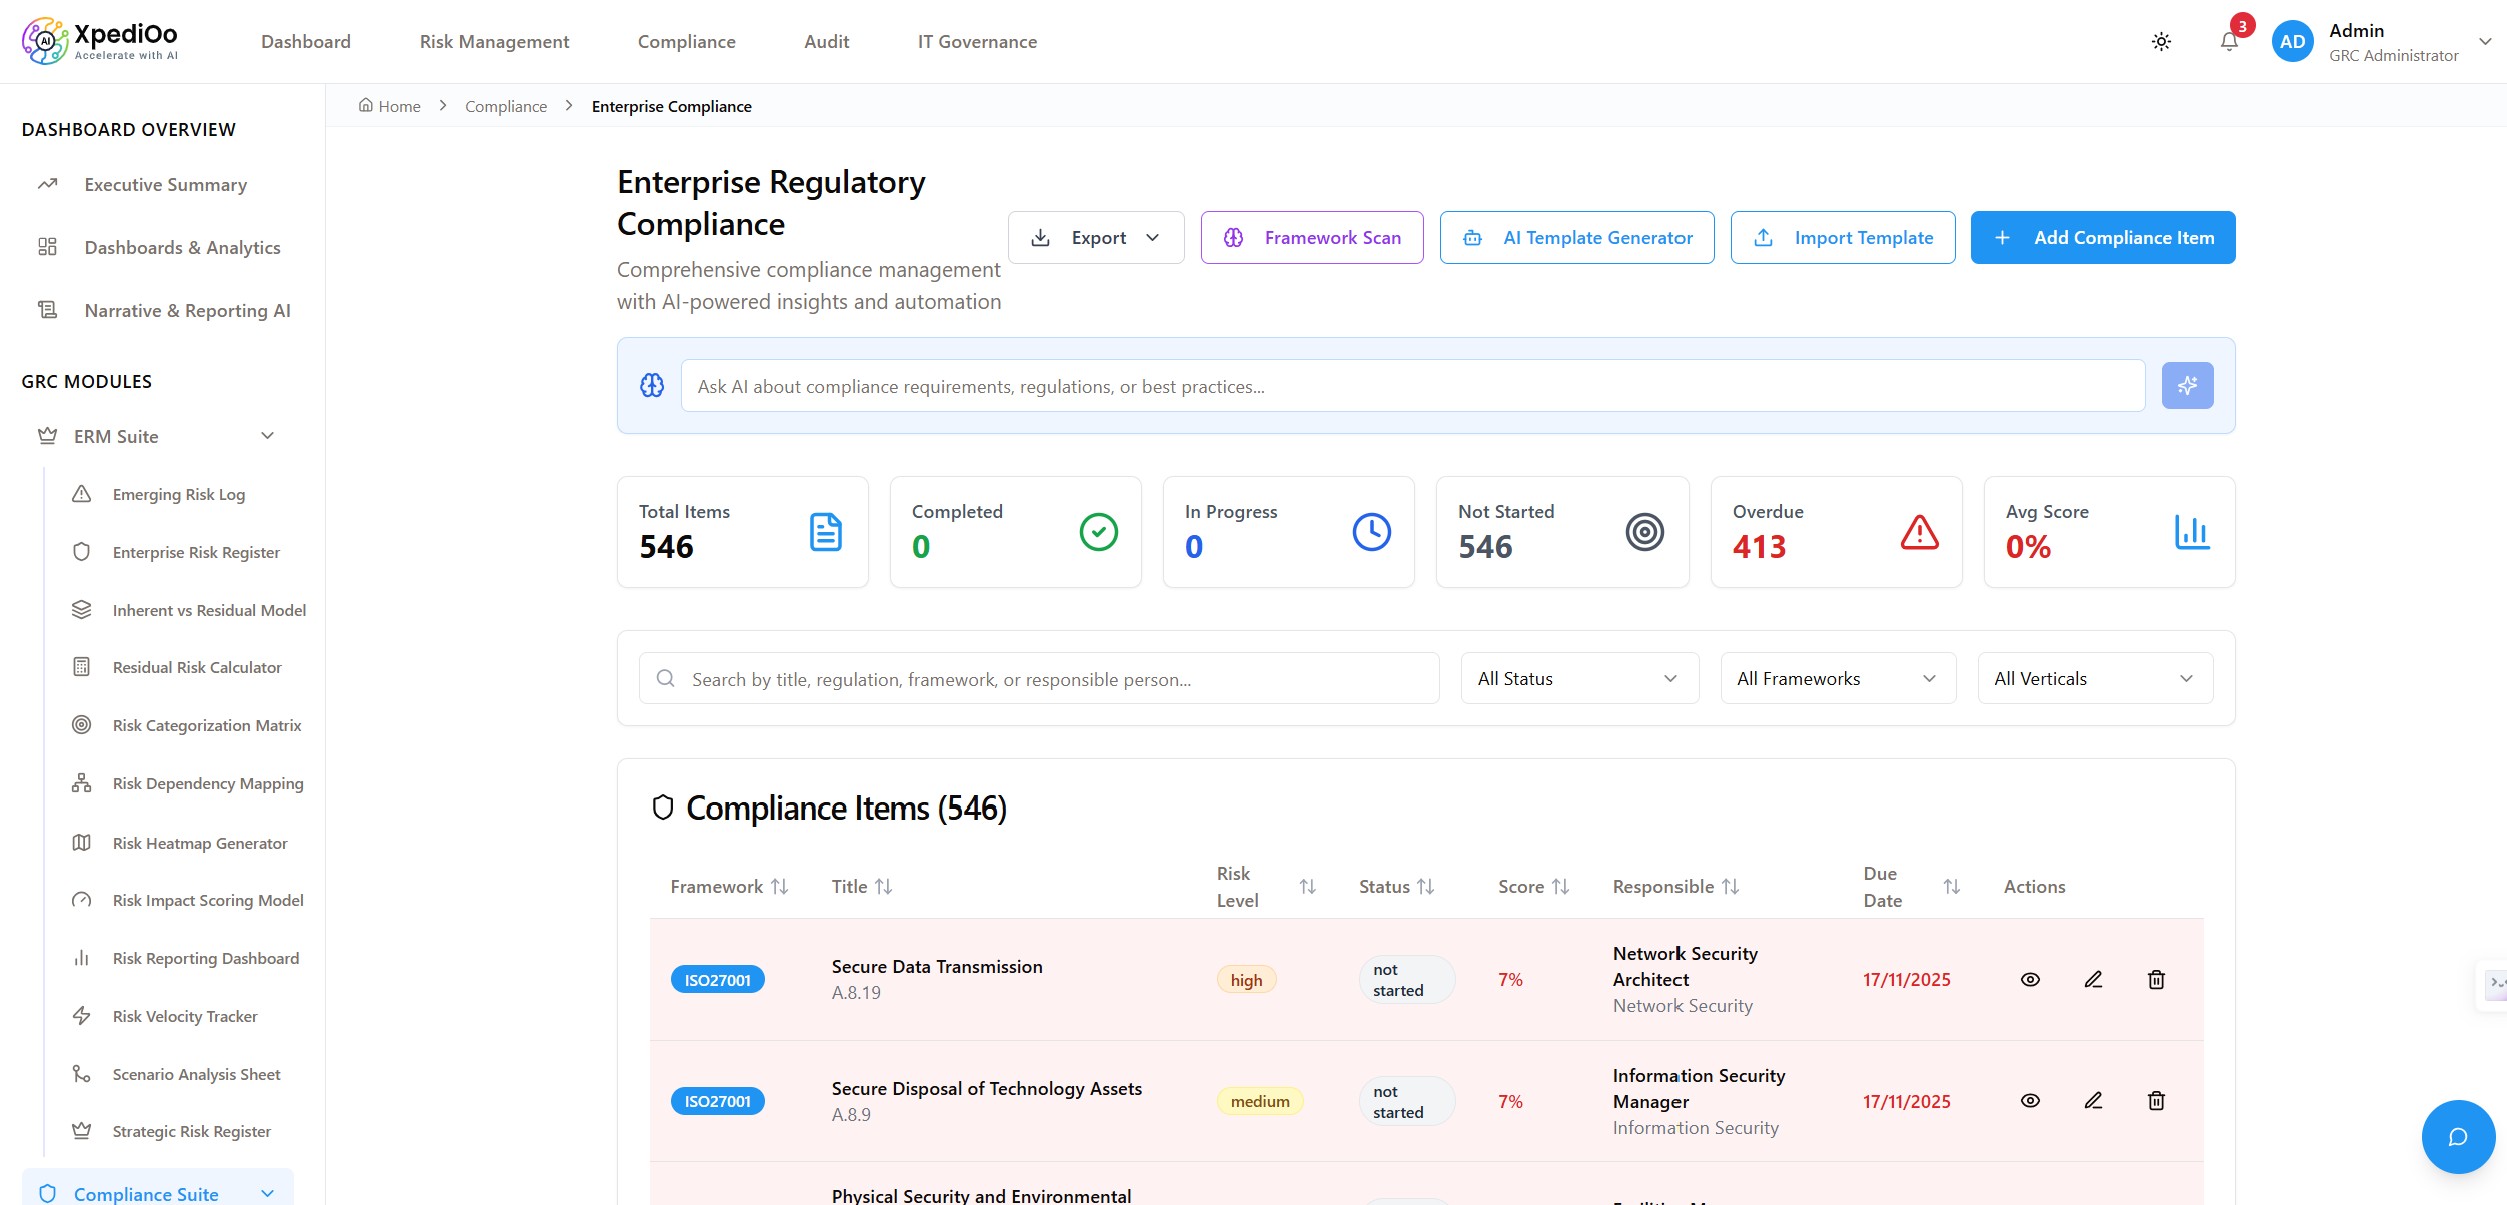
One workspace for every risk decision

Replace disconnected registers and point tools with a live, AI powered view of enterprise risk, compliance, cybersecurity, and board level performance.
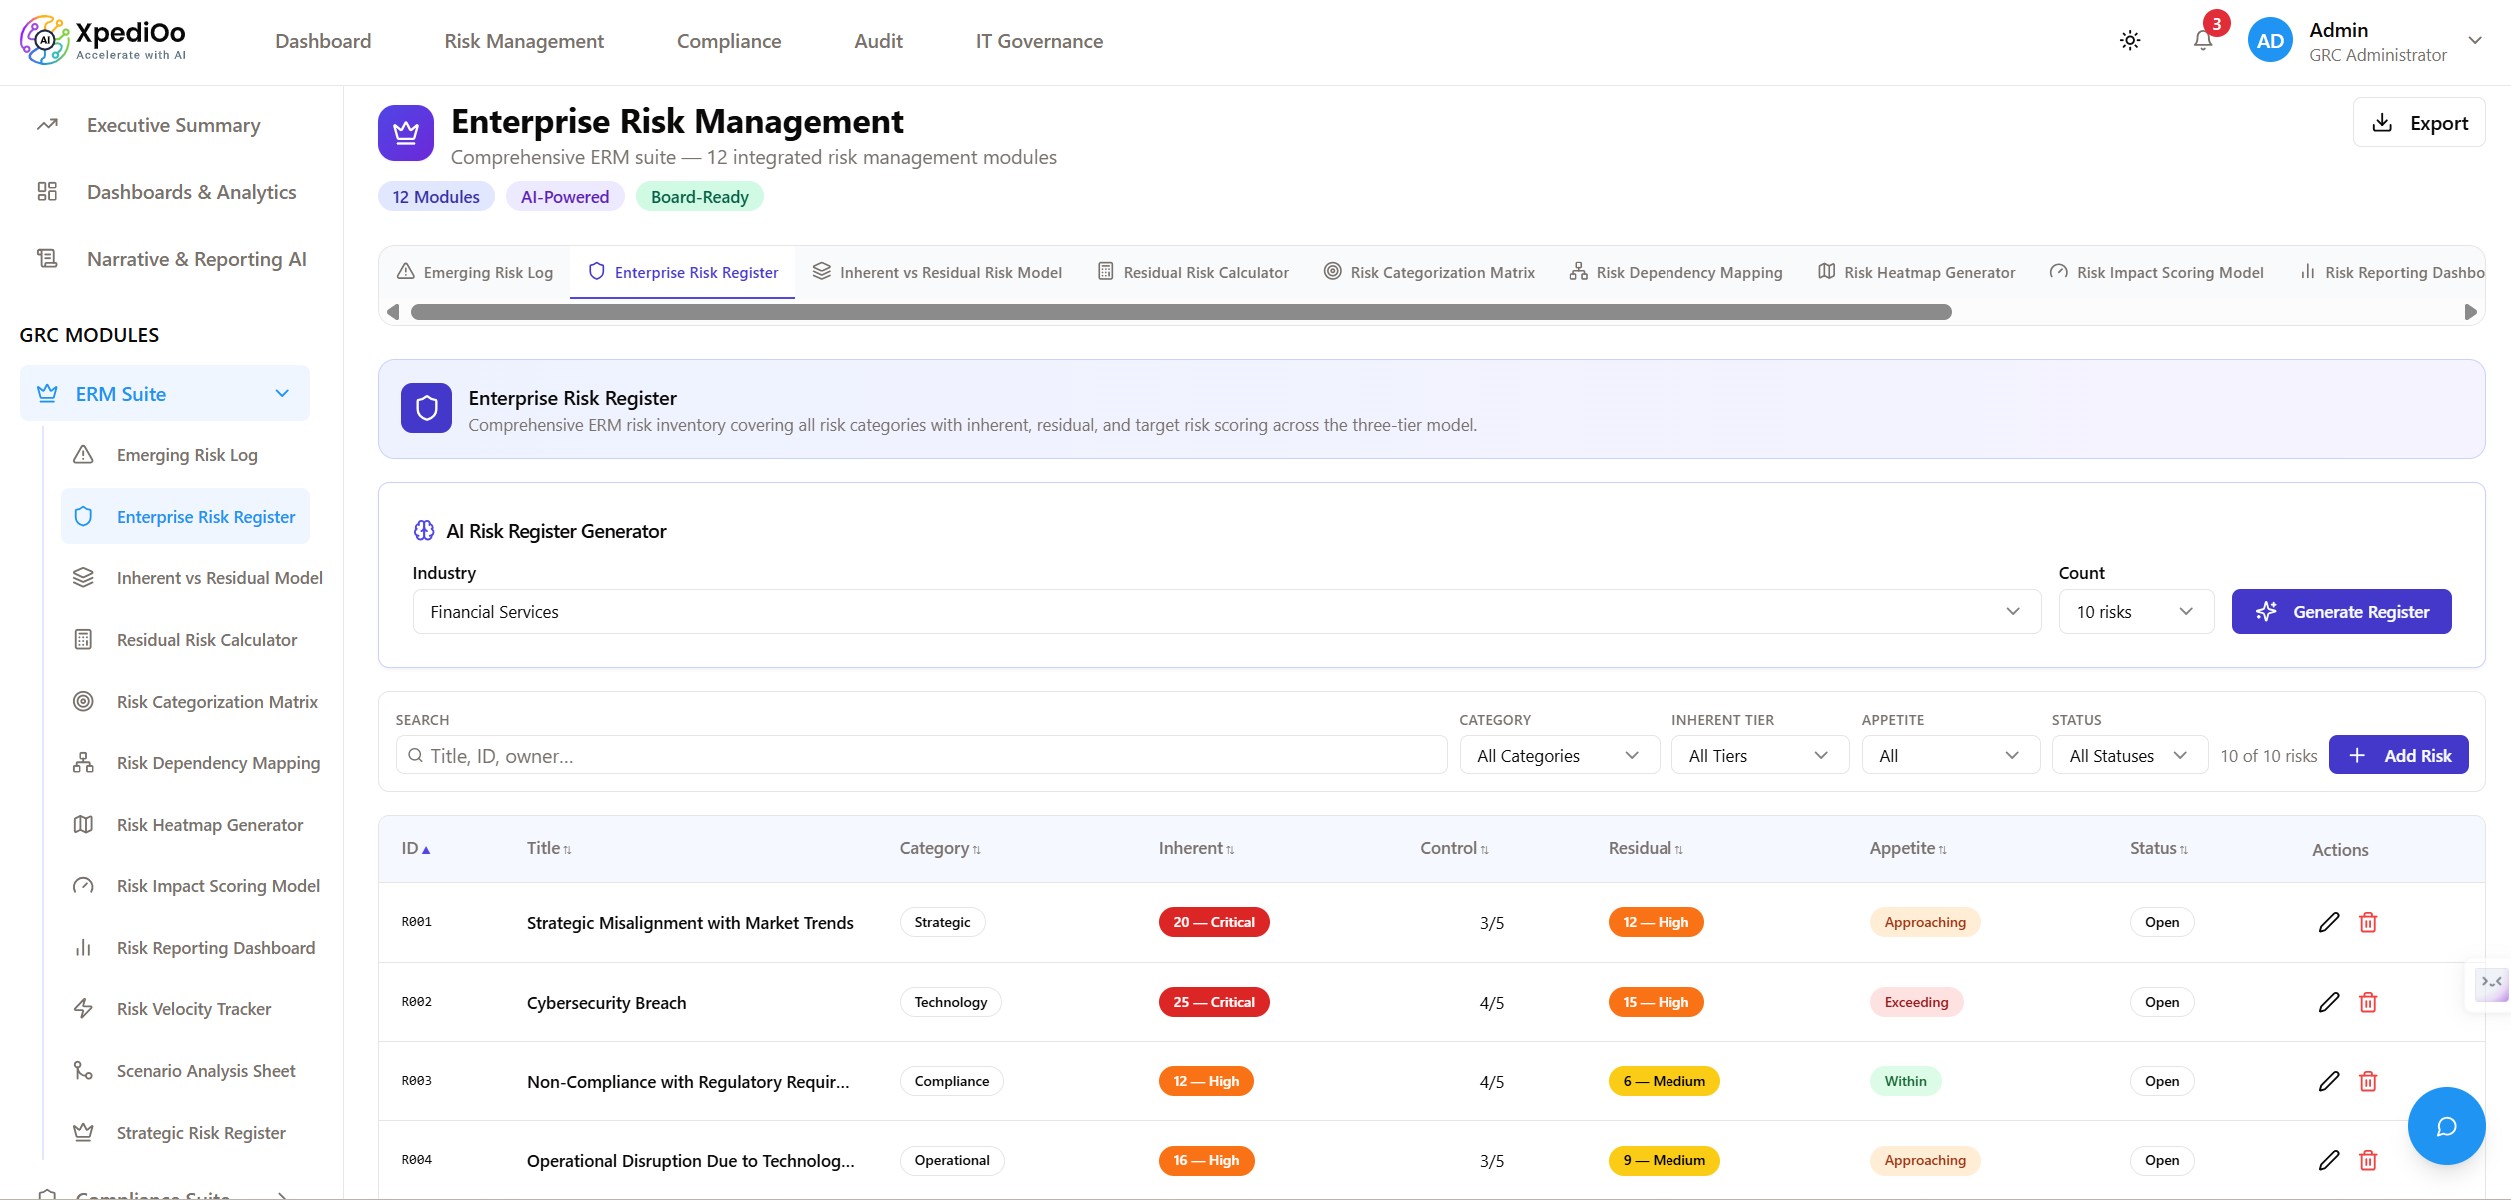
Enterprise Risk Register
XpediOo Enterprise Risk Register showing inherent, residual, and appetite risk scores
Module suites

20+ modules across six suites

Every module below lists capabilities in two tiers. Select a suite to explore its modules.

High impact:
AI driven or automation first, differentiating vs. legacy GRC tools
Standard:
comprehensive, audit grade system of record functionality

Third Party Risk Suite

AI accelerated vendor risk, contracts and due diligence.

5 modules

Vendor Register & Assessments

Central vendor register with onboarding, tiering, due diligence and questionnaire management for every third party.

High impact
  • AI generated, unlimited vendor questionnaire questions layered on predefined controls, including targeted AI/ML governance and cloud supply chain prompts
  • AI Vendor Assessment reads actual questionnaire responses to produce risk level, score, and a Security/Compliance/Financial/Operational breakdown
  • AI generated due diligence reports covering Executive Summary, Risk Analysis, Compliance Status, Findings and Recommendations
  • Nine prebuilt compliance questionnaire templates (TPRM, InfoSec, Financial Due Diligence, ISO 27001, SOC 2, SOX, PCI DSS, HIPAA, NIST CSF) with AI expansion
Standard
  • Vendor CRUD with tier, risk level, status, data access level, country, frameworks, owner and notes
  • Search with multiple filters by category, risk, status and tier; dashboard charts for vendor distribution and risk posture
  • Assessment and questionnaire response records with completion tracking

Concentration Risk Analyzer

Identifies single source, spend, geographic and revenue at risk vendor dependencies before they become crises.

High impact
  • Per exposure and portfolio level AI analysis producing executive summary, key findings, regulatory exposure and mitigation plans
  • Automated warnings for single source vendors with no alternatives and high criticality vendors with no supporting evidence
Standard
  • Exposure register with criticality tier, dependency level, substitute readiness, spend % and revenue at risk %
  • Spend vs revenue impact bubble chart and risk rating distribution with configurable thresholds

Contracts, SLAs & Supplier Scoring

Contract lifecycle, live SLA monitoring and a seven domain weighted supplier scorecard.

High impact
  • AI powered contract obligation analysis and compliance scoring with renewal/expiry alerts and breach tracking
  • AI root cause analysis for SLA breaches with remediation guidance before penalty thresholds trigger
  • AI weighted supplier ratings across Financial, Cybersecurity, Operational, Reputational, Geopolitical, ESG and Compliance domains
Standard
  • Contract register (MSA/SLA/NDA/DPA/SOW/licence) with renewal terms and breach detail
  • SLA metric register with target vs. actual tracking
  • Supplier scorecard with per domain scores, trend and review cadence

Third Party Risk Register & Assessment Templates

Formal inherent/residual risk register and repeatable vendor assessment methodology.

High impact
  • AI powered risk assessment and mitigation planning across ten risk categories, with inherent vs residual scoring
  • Structured control scoring across Information Security, Data Privacy, Business Continuity, Compliance, Financial Viability and Subcontractor Management
Standard
  • Risk register with likelihood/impact, treatment, owner and control effectiveness
  • Six assessment templates (Standard, Enhanced Due Diligence, Critical Vendor, IT/Cyber, Financial Stability, ESG)

Vendor Document Repository & Self Service Portal

A shared evidence store and a no login vendor portal that turns due diligence into self service.

High impact
  • AI reads uploaded evidence and flags whether it meets due diligence expectations, with a one click compliance check
  • AI generates a fully custom questionnaire from vendor context and emails a unique, no login portal link
  • Automatic response scoring, AI risk review and AI evidence compliance scanning
Standard
  • Central document repository with category, expiry date and status
  • Questionnaire register with due dates, auto score and submitted/reviewed state
  • Notification centre for due/expiring items, breaches and missing evidence
Why XpediOo

Built AI first, not AI bolted on

Legacy GRC suites added a chatbot on top of static registers. XpediOo starts from the AI layer and builds every workflow around it: vendor onboarding, audit scoring, policy drafting, board reporting.
Vendor questionnaires
Legacy GRC platformsStatic template library, manual review
XpediOo GRC & ERM SuiteAI generated per vendor, auto scored, AI reviewed evidence
Audit findings & KPIs
Legacy GRC platformsManual drafting; fixed KPI templates
XpediOo GRC & ERM SuiteAI drafted findings; AI suggested, IIA aligned KPIs on demand
Policy vs. framework mapping
Legacy GRC platformsManual crosswalk spreadsheets
XpediOo GRC & ERM SuiteAI generated crosswalks with evidence & bulk import
Board & regulator reporting
Legacy GRC platformsManual compilation from multiple systems
XpediOo GRC & ERM SuiteOne click AI narrative from live risk/compliance/audit data
AI/ML model governance
Legacy GRC platformsNot natively supported
XpediOo GRC & ERM SuiteRegistry aligned to RBI MRM Guidance 2026, with AI assessment
AI provider choice
Legacy GRC platformsLocked to a single vendor AI
XpediOo GRC & ERM Suite8 supported providers, bring your own key, swappable anytime
"The difference isn't that XpediOo has AI features. It's that AI removes the busywork from every register a GRC team already keeps, so analysts spend their time on judgement, not data entry."
Stakeholder value

Built for every seat at the risk table

One platform, six very different daily workflows, each accelerated by the same shared AI layer.

Chief Risk Officer

Sees enterprise risk exposure, appetite breaches and stress test outcomes in one view, with AI drafted board reports replacing manual data compilation before every risk committee.

Chief Compliance Officer

Tracks framework compliance rates, obligations and regulatory change in real time, with AI generated requirement templates and one click regulatory filing drafts for MAS, FCA, DORA, GDPR and more.

Head of Internal Audit

Runs a fully risk based audit plan with AI scored prioritisation, AI drafted findings and an AI suggested KPI scorecard, cutting the manual drafting time behind every audit report.

Chief Information Security Officer

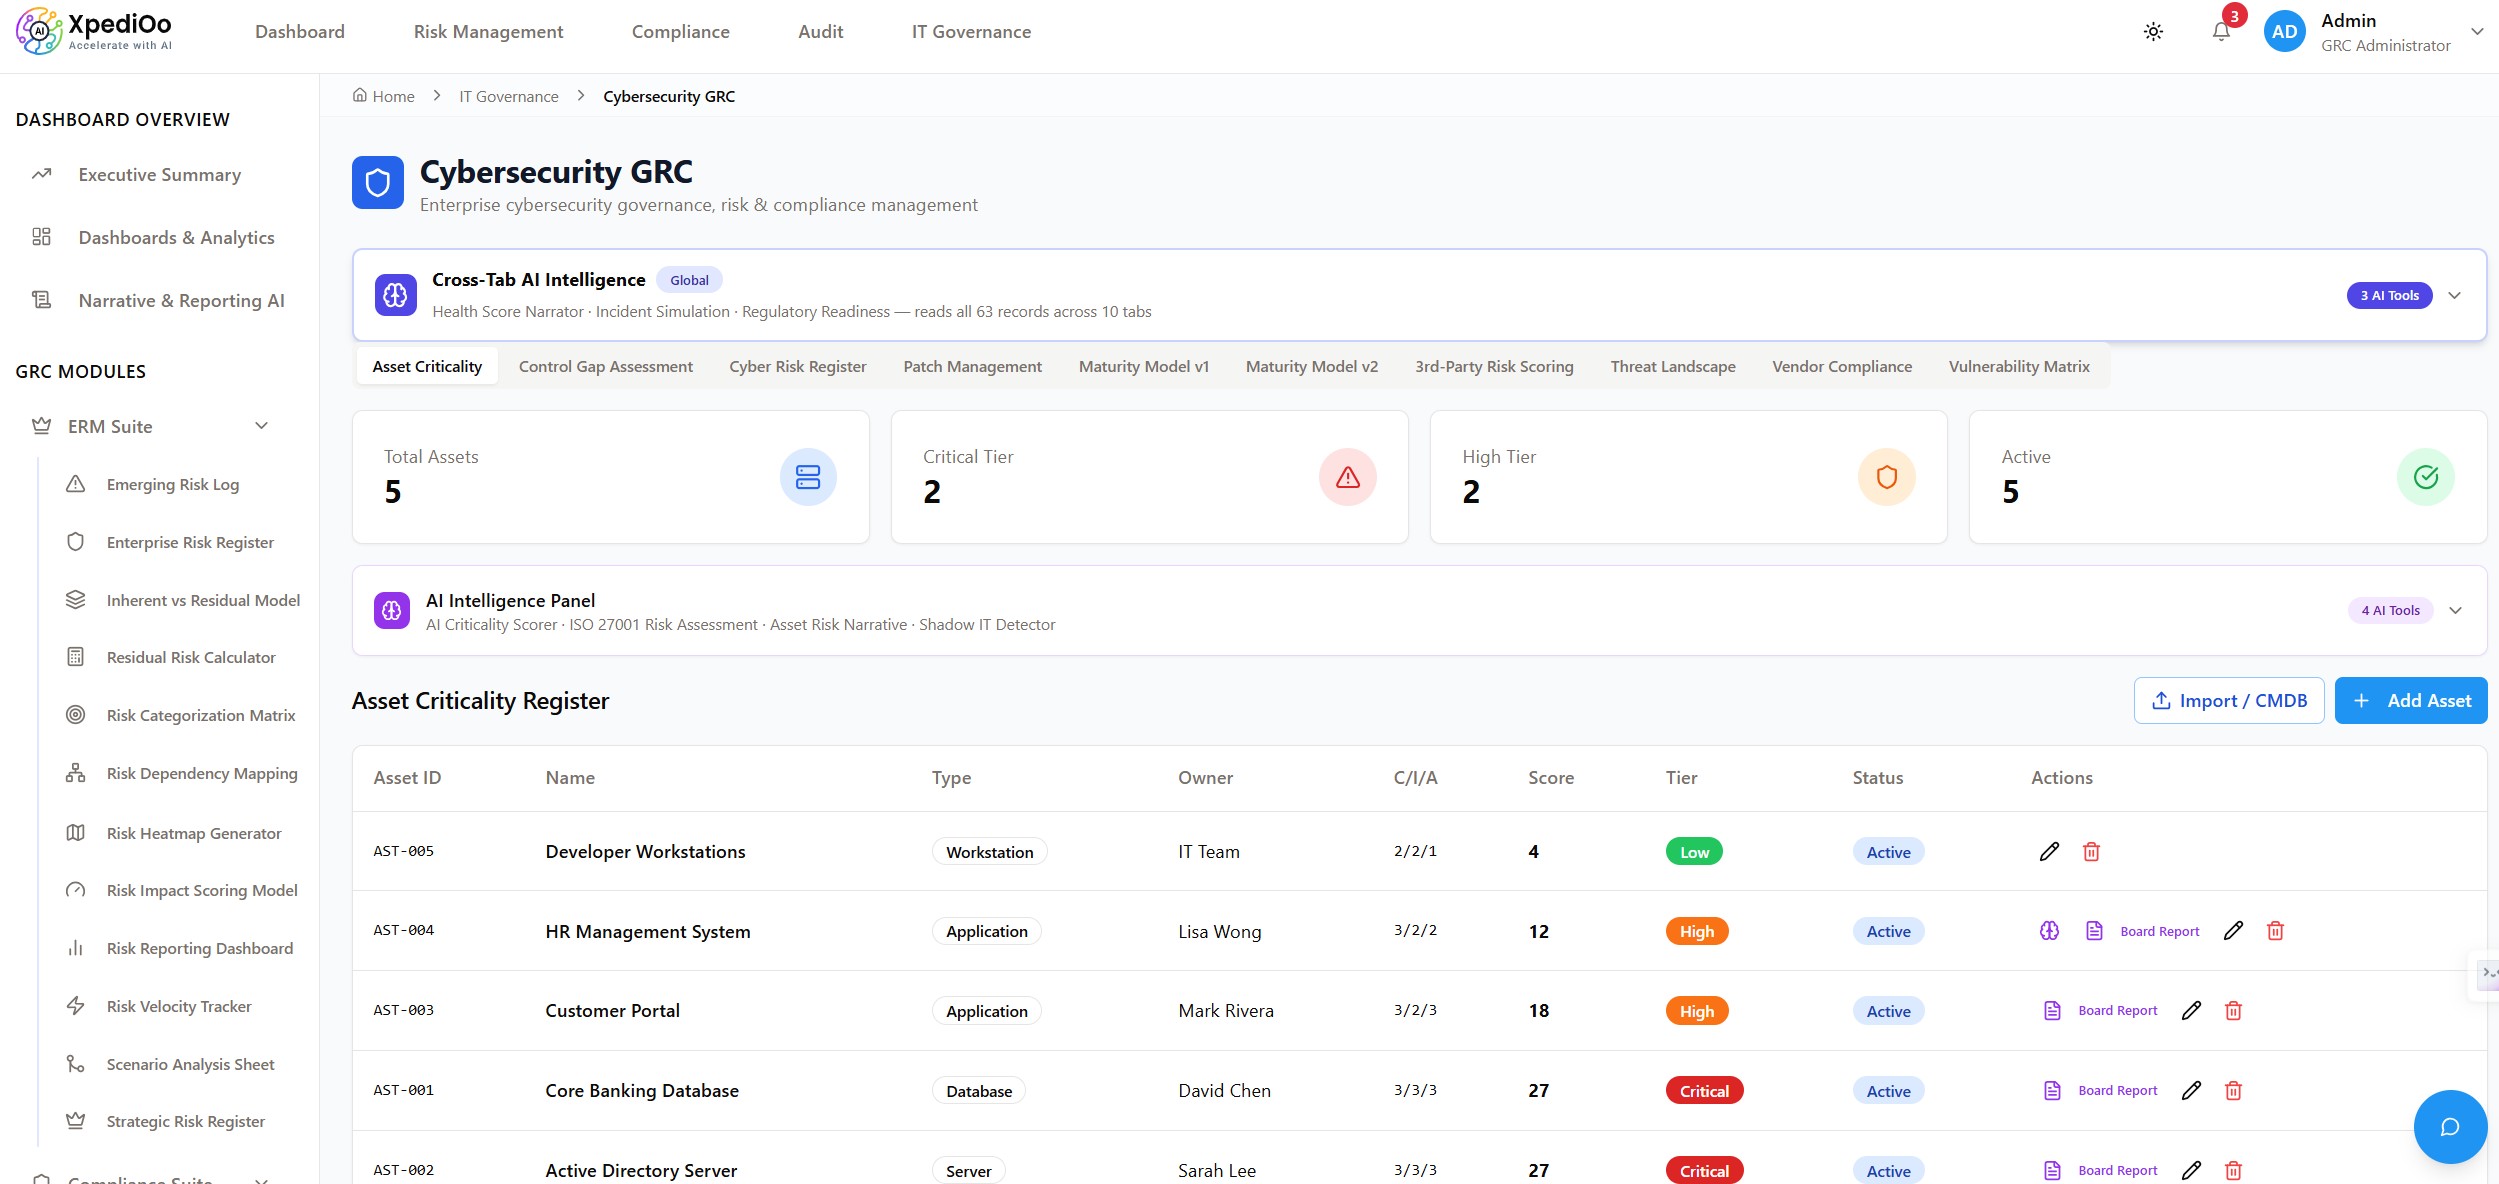
Uses AI asset criticality scoring, ISO 27001 gap assessment and vulnerability triage to turn a sprawling CMDB into a prioritised, board ready cyber risk narrative.

Head of Procurement / TPRM

Sends AI generated, vendor specific due diligence questionnaires through a no login portal and gets an AI risk assessment the moment a vendor responds. No manual scoring spreadsheet required.

Model Risk / AI Governance Lead

Maintains a model inventory aligned to RBI MRM Guidance 2026, with AI assisted tiering, explainability and bias testing coverage tracking for every AI/ML model in production.

AI patterns

AI capability glossary

The same handful of AI capability patterns repeat across every module. Understanding them once makes the whole platform predictable.

AI Scoring

Converts qualitative inputs (a vendor profile, a control description, an incident) into a defensible, weighted numeric score. Used for vendor risk, supplier scorecards, audit prioritisation and cyber asset criticality.

AI Drafting

Generates a first draft narrative (an audit finding, a management action plan, a board report, a regulatory filing) from structured record data, for a human reviewer to refine and approve.

AI Generation / Templating

Produces a complete starting record set (a questionnaire, a compliance requirement template, an ESG risk register, a model inventory) tailored to industry, framework or context, ready for bulk import.

AI Gap / Compliance Analysis

Compares an artefact (a policy, an evidence file, a control set) against a named framework or objective and reports coverage, gaps and remediation steps.

AI Extraction

Reads unstructured documents (contracts, regulations, meeting minutes) and pulls out structured obligations, dates, owners and risks.

AI Portfolio Intelligence

Analyzes an entire register at once, rather than one record at a time, producing an executive summary, priority actions and portfolio level risk level.

AI Compliance Generator

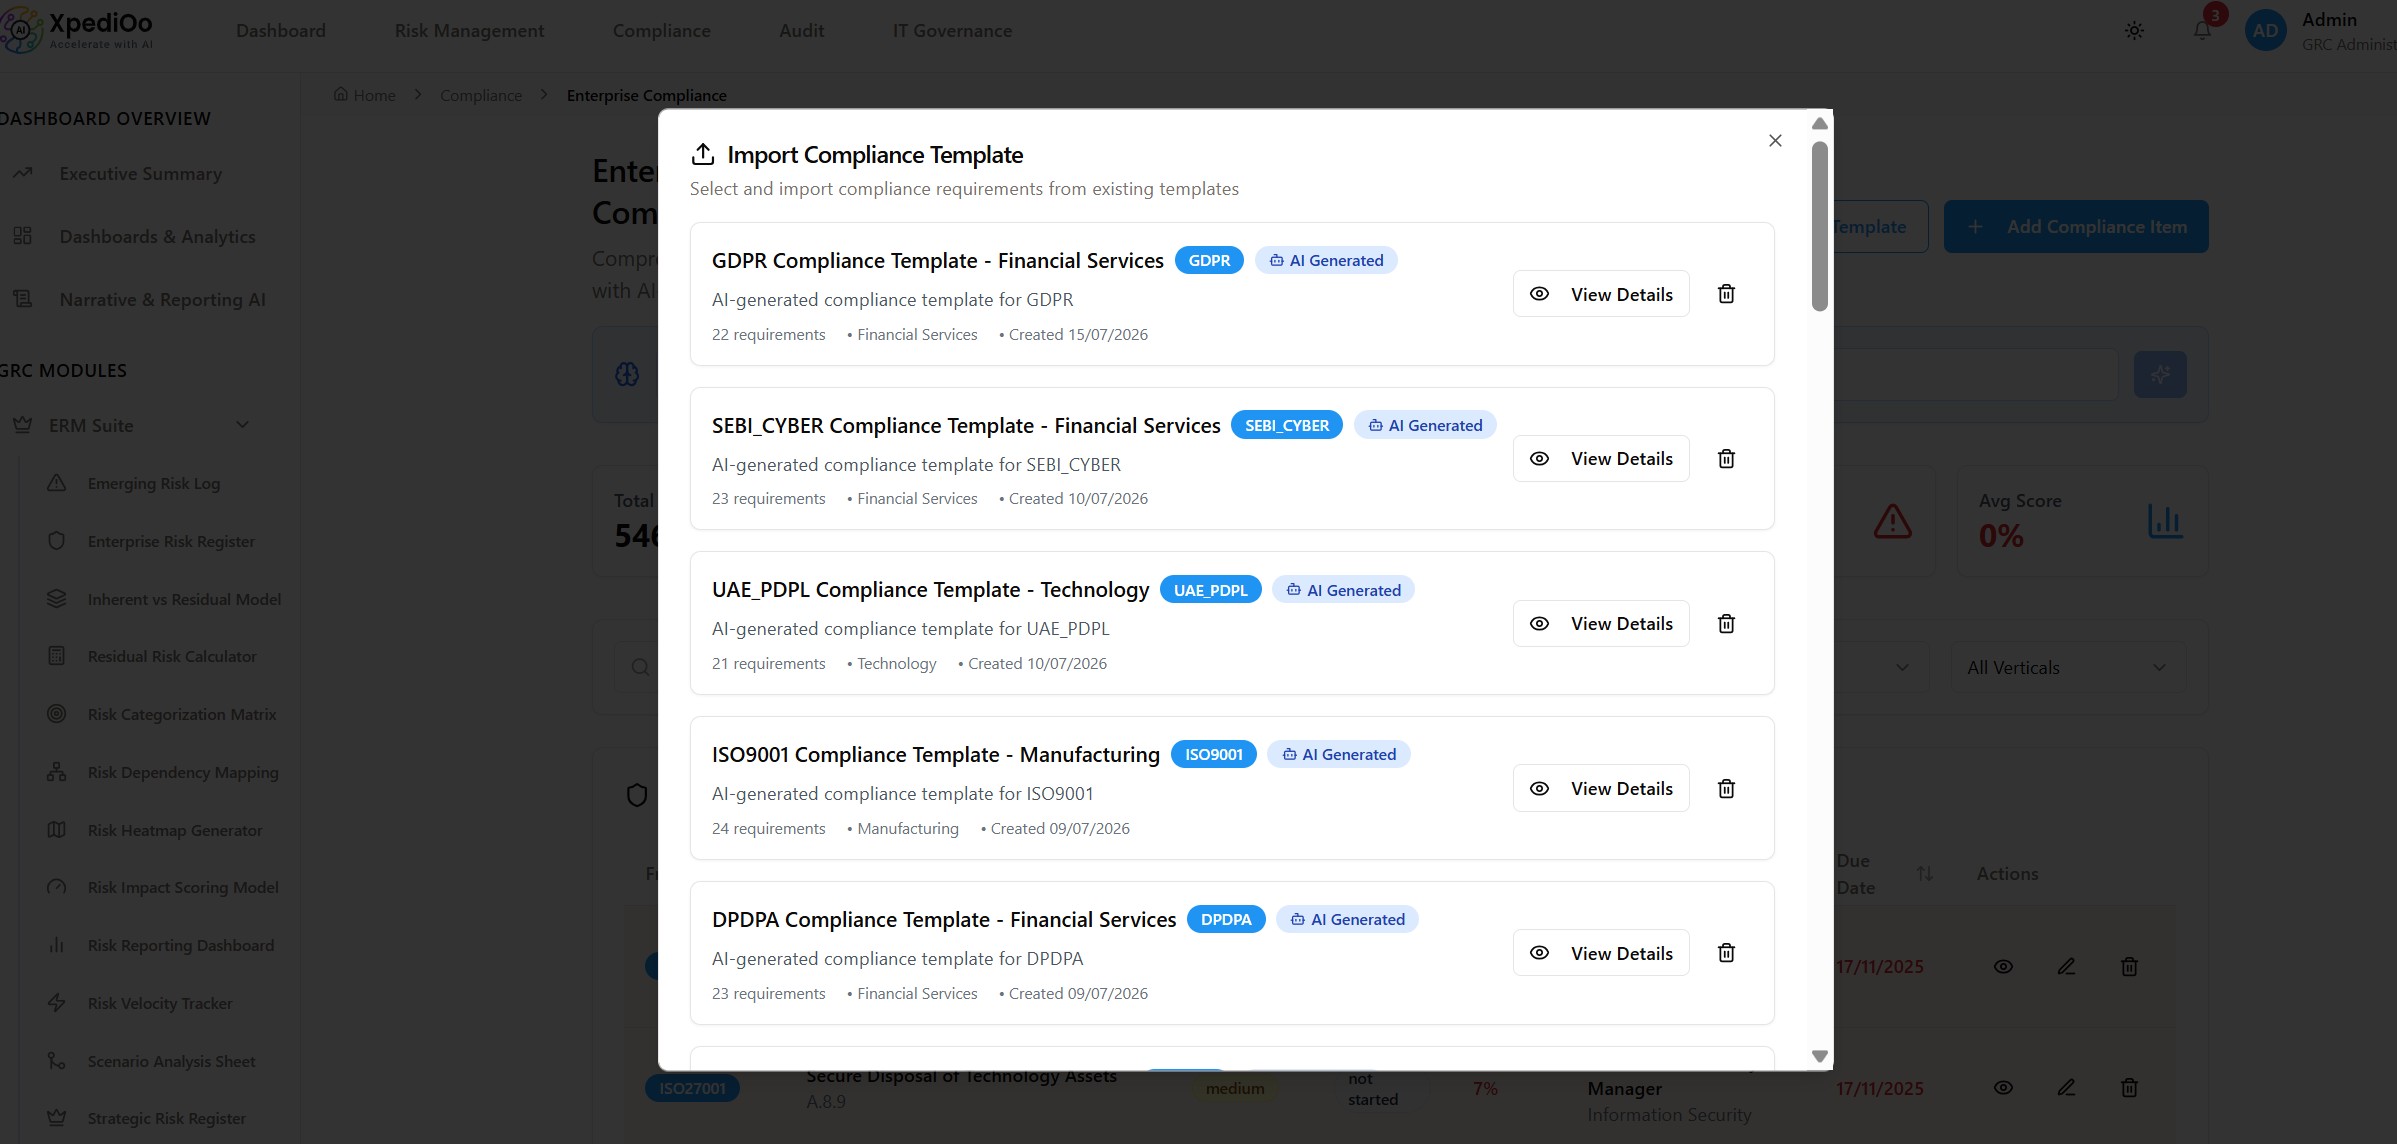
210 implemented frameworks in the AI Compliance Generator

The catalog below lists every framework implemented in the AI Compliance Generator, grouped into 40 categories. The generator produces an evidence based compliance report with a compliance score, executive summary, findings, root cause and remediation. Descriptions summarize each framework's scope.

Showing 210 of 210 frameworks

Implementation

A phased path to value

Organisations typically light up XpediOo in three phases, expanding from a single high pain module to full GRC/ERM coverage.
01

Foundation

Stand up the core register(s) for the highest priority pain point (commonly Third Party Risk or Internal Audit), migrate existing spreadsheets, configure the LLM provider, and connect the object storage evidence layer.

Phase 1Weeks 1–4
02

Automate

Turn on AI assessment, scoring and drafting for the live register; enable the self service vendor portal or AI questionnaire generation; connect Compliance, Audit and Risk registers so cross module warnings start firing.

Phase 2Weeks 4–10
03

Scale

Extend to remaining suites (Governance, Privacy, Business Continuity, Cybersecurity GRC, Model Risk), activate Board Reporting and Narrative AI, and open the MCP server to approved internal AI copilots.

Phase 3Ongoing
Industries

Industries we serve

The framework coverage and module design reflect these sectors in particular, though configurable frameworks and AI generated templates extend to any regulated industry.
01

Banking and financial services

RBI Model Risk Management Guidance 2026, MAS TRM, FCA, PRA, DORA, FINMA, APRA and SEC coverage fit banks, NBFCs, insurers and asset managers managing model risk, third party risk and regulator reporting simultaneously.

02

Technology and SaaS

SOC 2, ISO 27001, GDPR and PCI DSS coverage, plus the AI/ML model registry and shadow IT detection, fit vendor heavy, cloud native organisations that must prove security and privacy posture to enterprise customers.

03

Healthcare and life sciences

HIPAA aligned compliance tracking and the Privacy Suite's breach, ROPA and retention workflows support covered entities and business associates managing protected health information.

04

Government and public sector

ISO 31000/9001/14001/22301 and jurisdiction specific privacy frameworks (UAE PDPL, PIPEDA) support agencies running formal enterprise risk and business continuity programmes.

05

Manufacturing and critical infrastructure

Business Continuity, Financial Controls and Cybersecurity GRC modules (including CMDB based asset criticality scoring) support operationally complex, supply chain dependent organisations.

FAQ

Frequently asked questions

Common questions from evaluation teams.

AI Powered GRC

Let's put this to work

XpediOo GRC & ERM Suite is ready to evaluate against your current registers, spreadsheets and point tools, through a live walkthrough, a proof of concept, or a full module by module RFP response.

Contact sales